

Your fleet data is business-critical. TrailerSmart is designed with controlled access, data protection and operational accountability at its core.

Secure by Design
TrailerSmart uses layered access controls and company-level data isolation to ensure users only access the information and functionality authorised for their organisation and role.
- Layered access controls
- Company-level isolation
- HTTPS encryption


Role-Based Access
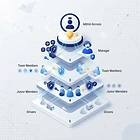
Permissions can be controlled according to operational responsibility, helping ensure drivers, planners, managers and administrators only access the areas appropriate to their role.
- Six role types
- Operational responsibility
- Depot scoping

Company Data Isolation
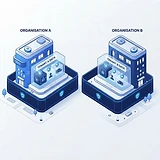
Customer information is logically separated within the TrailerSmart platform and access controls are applied throughout the system to prevent unauthorised cross-company access.
- Logical separation
- No cross-access
- Enforced at data layer

Auditability
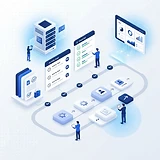
Important operational and administrative actions can be recorded within TrailerSmart to provide greater visibility and accountability.
- Attributable actions
- Before & after values
- Admin-only deletion
Six layers of protection
Security is enforced at the data layer on every request — not simply hidden in the interface.

Role-Based Access
Every user receives access appropriate to their role — from Super Admin down to Driver.
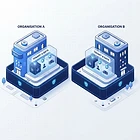
Company Data Separation
Drivers, trailers, compliance, customers and operational records stay within your organisation.


Database-Level Security
Controls are enforced at the data layer on every request — not just hidden in the interface.

Secure Document Access
Compliance documents, MOT records and inspection photos are accessed through authenticated sessions.


Audit Trail
Creates, updates and deletes are recorded with user, company, timestamp and the record affected.

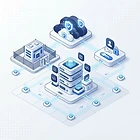
Platform Infrastructure
TrailerSmart is delivered as a managed platform with secure hosting, authentication and infrastructure handled as part of the service.
What we protect
Each category is handled through controlled access, separation and auditability.

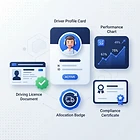
Driver Information
- Driver records
- Licence/compliance
- Allocations
- Performance

Fleet Information
- Tractor units
- Trailers
- Registrations
- Maintenance

Compliance Information
- MOT records
- Inspections
- Walk-around photos
- Defect reports


Business Information
- Customers
- Depots
- Collection plans
- Commercial data

Operational Information
- Utilisation
- KPIs
- Maintenance costs
- Call-outs
Access designed around your team
Access is determined by each user’s assigned role and evaluated at the data layer.
| Area | Super Admin | Company Admin | Fleet Manager | Dispatcher | Driver |
|---|---|---|---|---|---|
| Company Settings | Full | Full | — | — | — |
| Fleet | Full | Full | Full | Operational | Assigned |
| Drivers | Full | Full | Operational | Operational | Own |
| Compliance | Full | Full | Full | View | Own/Relevant |
| Inspections | Full | Full | Full | View | Own |
| Maintenance | Full | Full | Full | Operational | Relevant |
| Customers | Full | Full | Authorised | Operational | Assigned |
| Billing | Full | Full | — | — | — |
| Audit Log | Full | Authorised | Authorised | Limited | Own Activity |
Your data stays within your organisation
Every read, write and delete is filtered by the signed-in user’s company at the data layer.
Customer A
Organisation tenantRecords carry Customer A’s organisation identifier. Only authorised users within this organisation can access them.
Customer B
Organisation tenantRecords carry Customer B’s organisation identifier. Only authorised users within this organisation can access them.
Accountability built in
Important activity is recorded — capturing who performed an action, what was done, when, and which record was affected. Audit entries cannot be edited by ordinary users.
| Who | What | When | Company | Record |
|---|---|---|---|---|
| S. Patel | Created a driver | 29 Jul 2026 · 08:14 | Acme Logistics | Driver — J. Walker |
| M. Hughes | Changed a vehicle allocation | 29 Jul 2026 · 09:02 | Acme Logistics | Trailer — AB12 CDE |
| D. Okafor | Completed an inspection | 29 Jul 2026 · 09:47 | Acme Logistics | Inspection — #IN-10482 |
| R. Ali | Changed a customer rate | 29 Jul 2026 · 11:05 | Acme Logistics | Customer — Northgate |
| M. Hughes | Updated fuel surcharge | 29 Jul 2026 · 11:22 | Acme Logistics | Surcharge — Northgate |
Illustrative examples only. Each entry is tied to a named, authenticated user and their organisation.
Drivers see what they need. Nothing more.
The driver experience is deliberately focused — no administrative, commercial or other drivers’ private information is exposed.
Accessible to drivers
Focused operational access- Their assigned vehicle
- Their assigned trailer
- Their collections
- Their inspections
- Their defect reporting
- Relevant compliance tasks
Not exposed to drivers
Restricted by design- Other drivers' personal information
- Company billing
- Customer commercial rates
- Fuel surcharge information
- Administration settings
- Other companies' data
Controlled shared asset access
Tractor units and trailers can be shared between depots without transferring ownership. A shared depot sees only the operational access it has been granted.
Enforced at the data layer: access is determined by the asset’s owning depot and shared-access list — evaluated on every request.
- Compliance
- Maintenance
- MOT
- Service history
- Defect resolution
- Asset ownership
GDPR & Data Protection
Designed with data protection principles in mind. Role-based access, company-level separation and audit trails help customers control who can reach information.
Customers remain responsible for their own lawful basis for processing and legal obligations under applicable data protection law.
Data Retention & Deletion
Administrators can manage records and user access within their organisation in line with their own retention policies.
Critical compliance records and audit history cannot be deleted by ordinary users — preserving accountability.
Incident Management
Identify
Activity recorded in the audit trail.
Respond
Access reviewed by authorised admins.
Record
Actions captured in the audit log.
About our platform infrastructure
TrailerSmart is built with security and data protection at the core of the platform, using controlled authentication, role-based access and company-level data isolation to protect operational information. The controls described on this page — role-based access, company-level data separation, audit trails and document security — are TrailerSmart’s own application-layer controls, enforced at the data layer on every request. TrailerSmart has not independently obtained SOC 2, ISO 27001 or equivalent certification for its application at this time.
Common questions
Security you can ask us about
We believe security should be transparent. If you’re evaluating TrailerSmart for your fleet, we’re happy to discuss how access controls, company separation, auditability and data protection work within the platform.